
Appearance
Sign-in and tokens
This page is for: advisors, forward-deployed engineers and developers who connect AI tools or the CLI.
There are two ways to prove who you are: browser sign-in (OAuth) or a personal token. Both reach the same tools.
Browser sign-in
Built
MCP clients that support OAuth find DutyGraph's sign-in at /.well-known/oauth-authorization-server. You approve the connection in DutyGraph and the client gets a token for you.
- An advisor gets
readandwrite. - An employee gets
share_work, bound to their own person record. A leader also getsshare_strategy. - The CLI uses this flow with a callback on your own machine.
Browser sign-in never grants email sending.
Personal tokens
Built
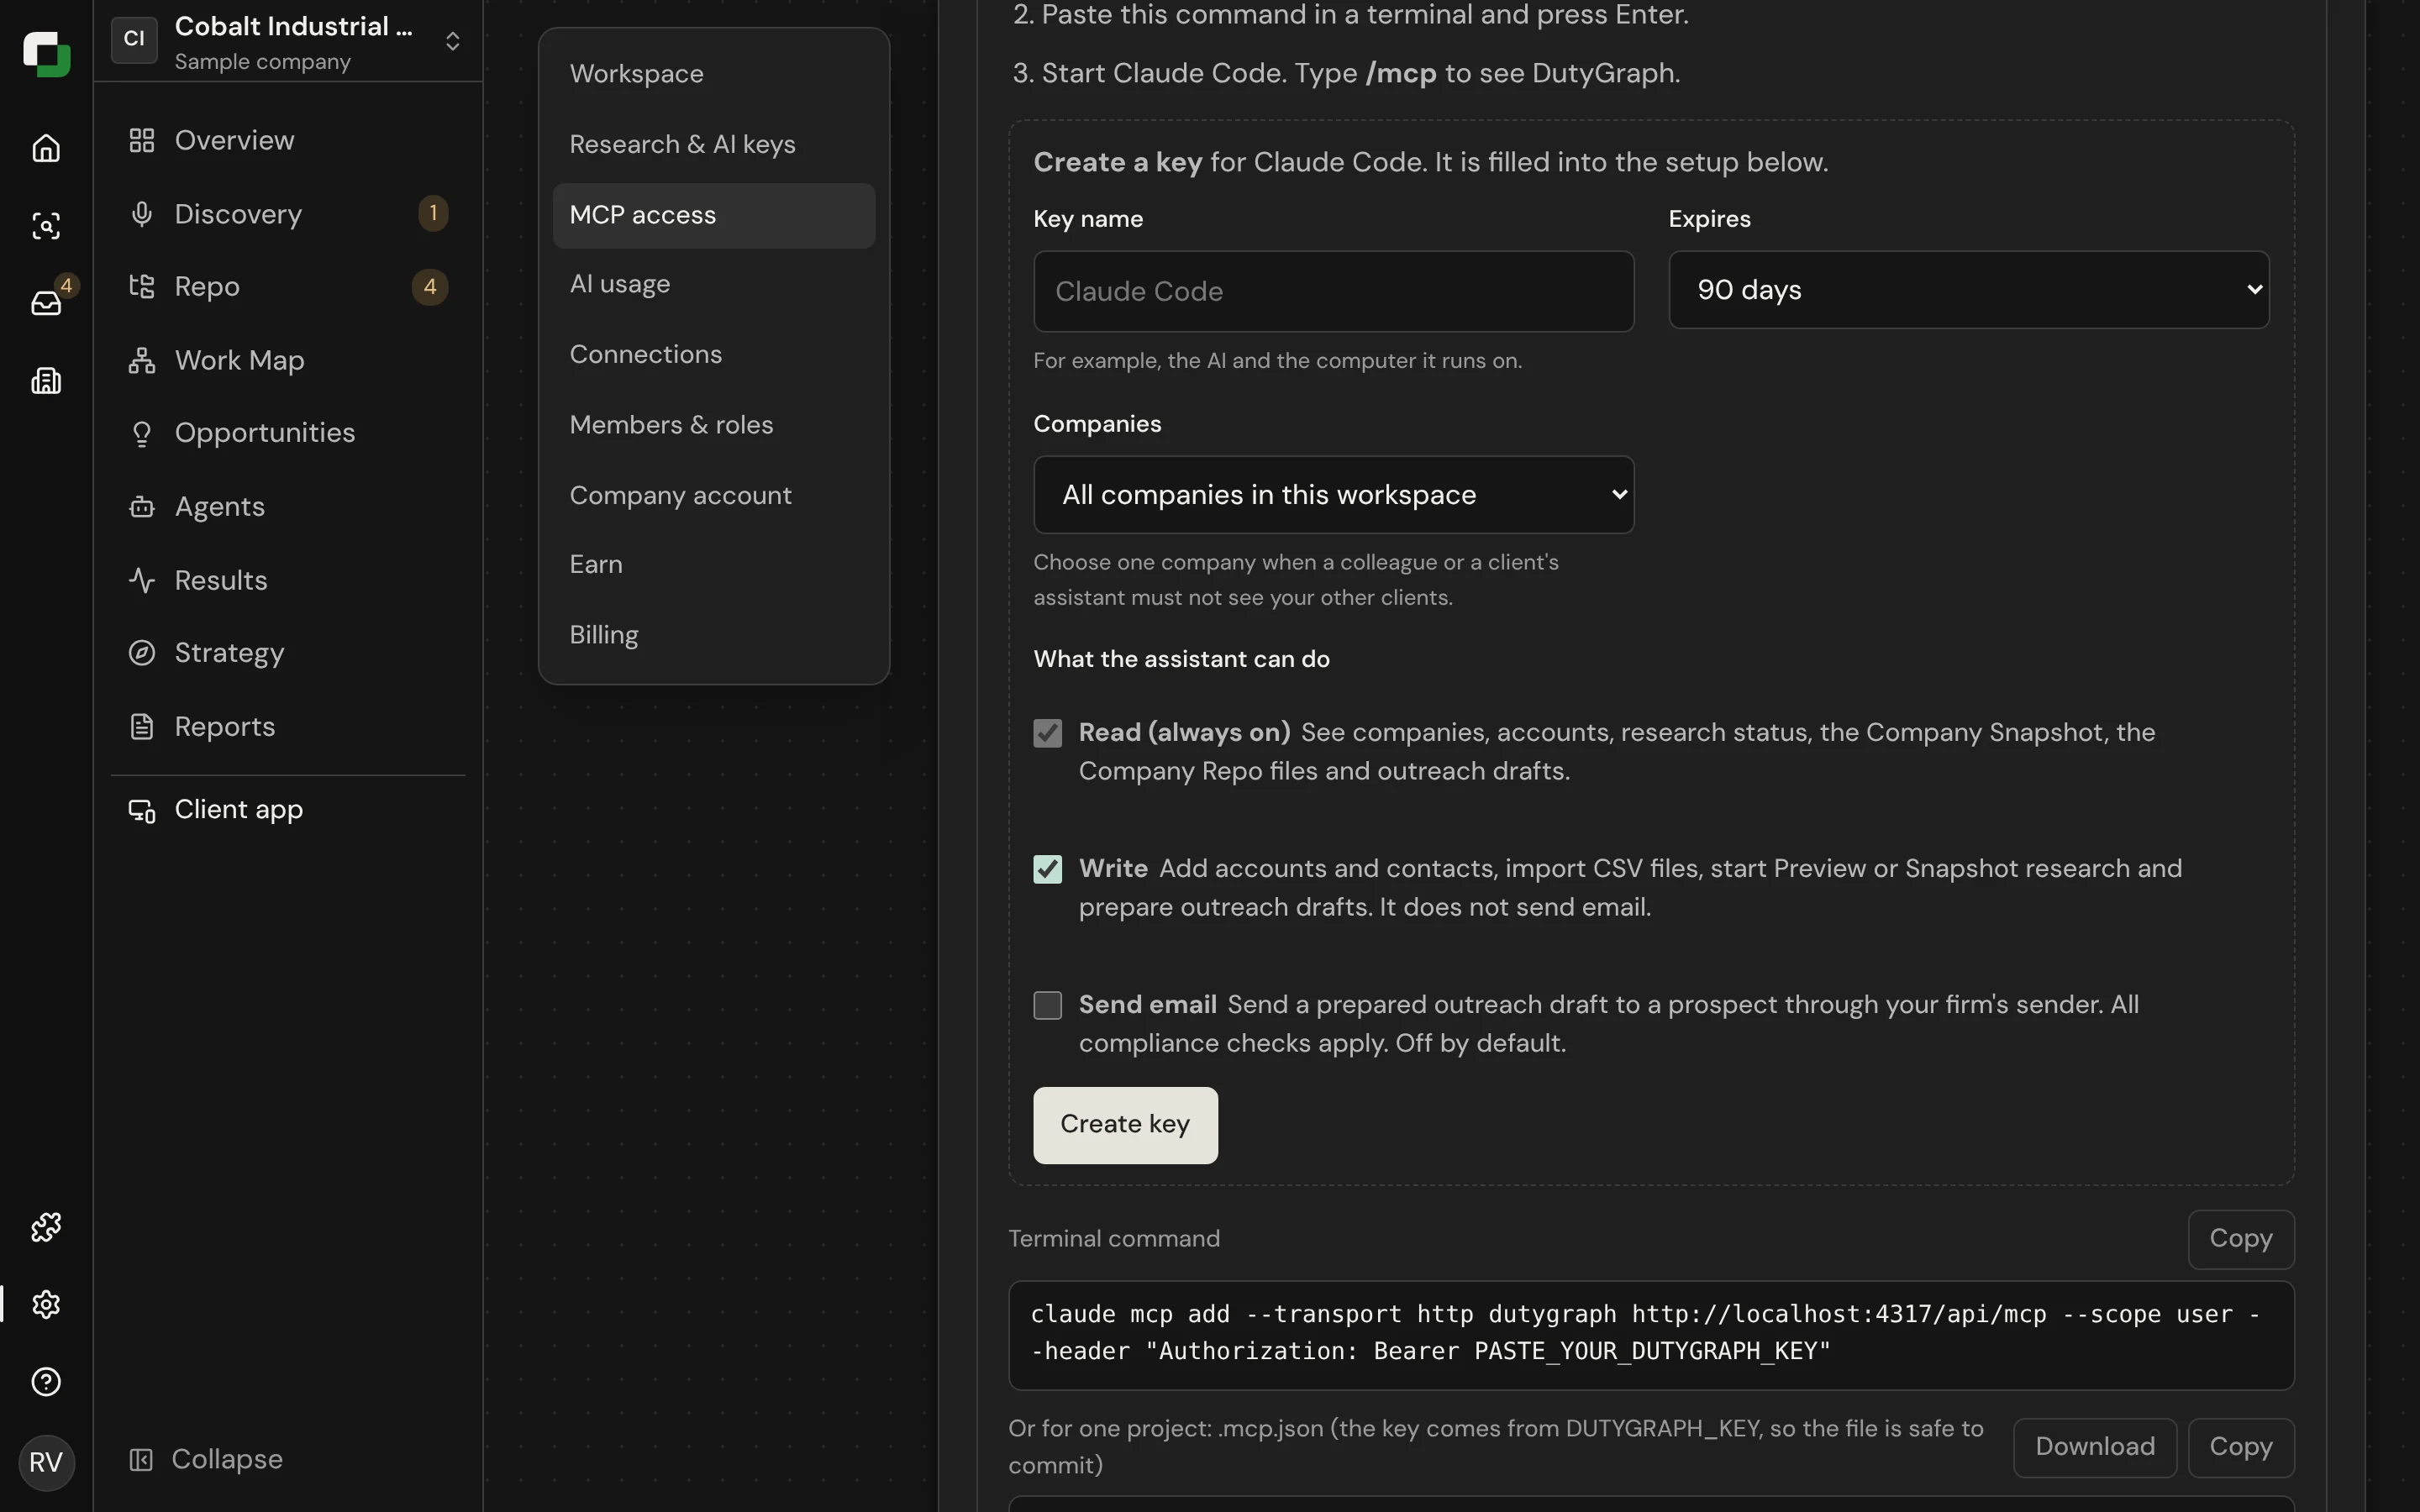
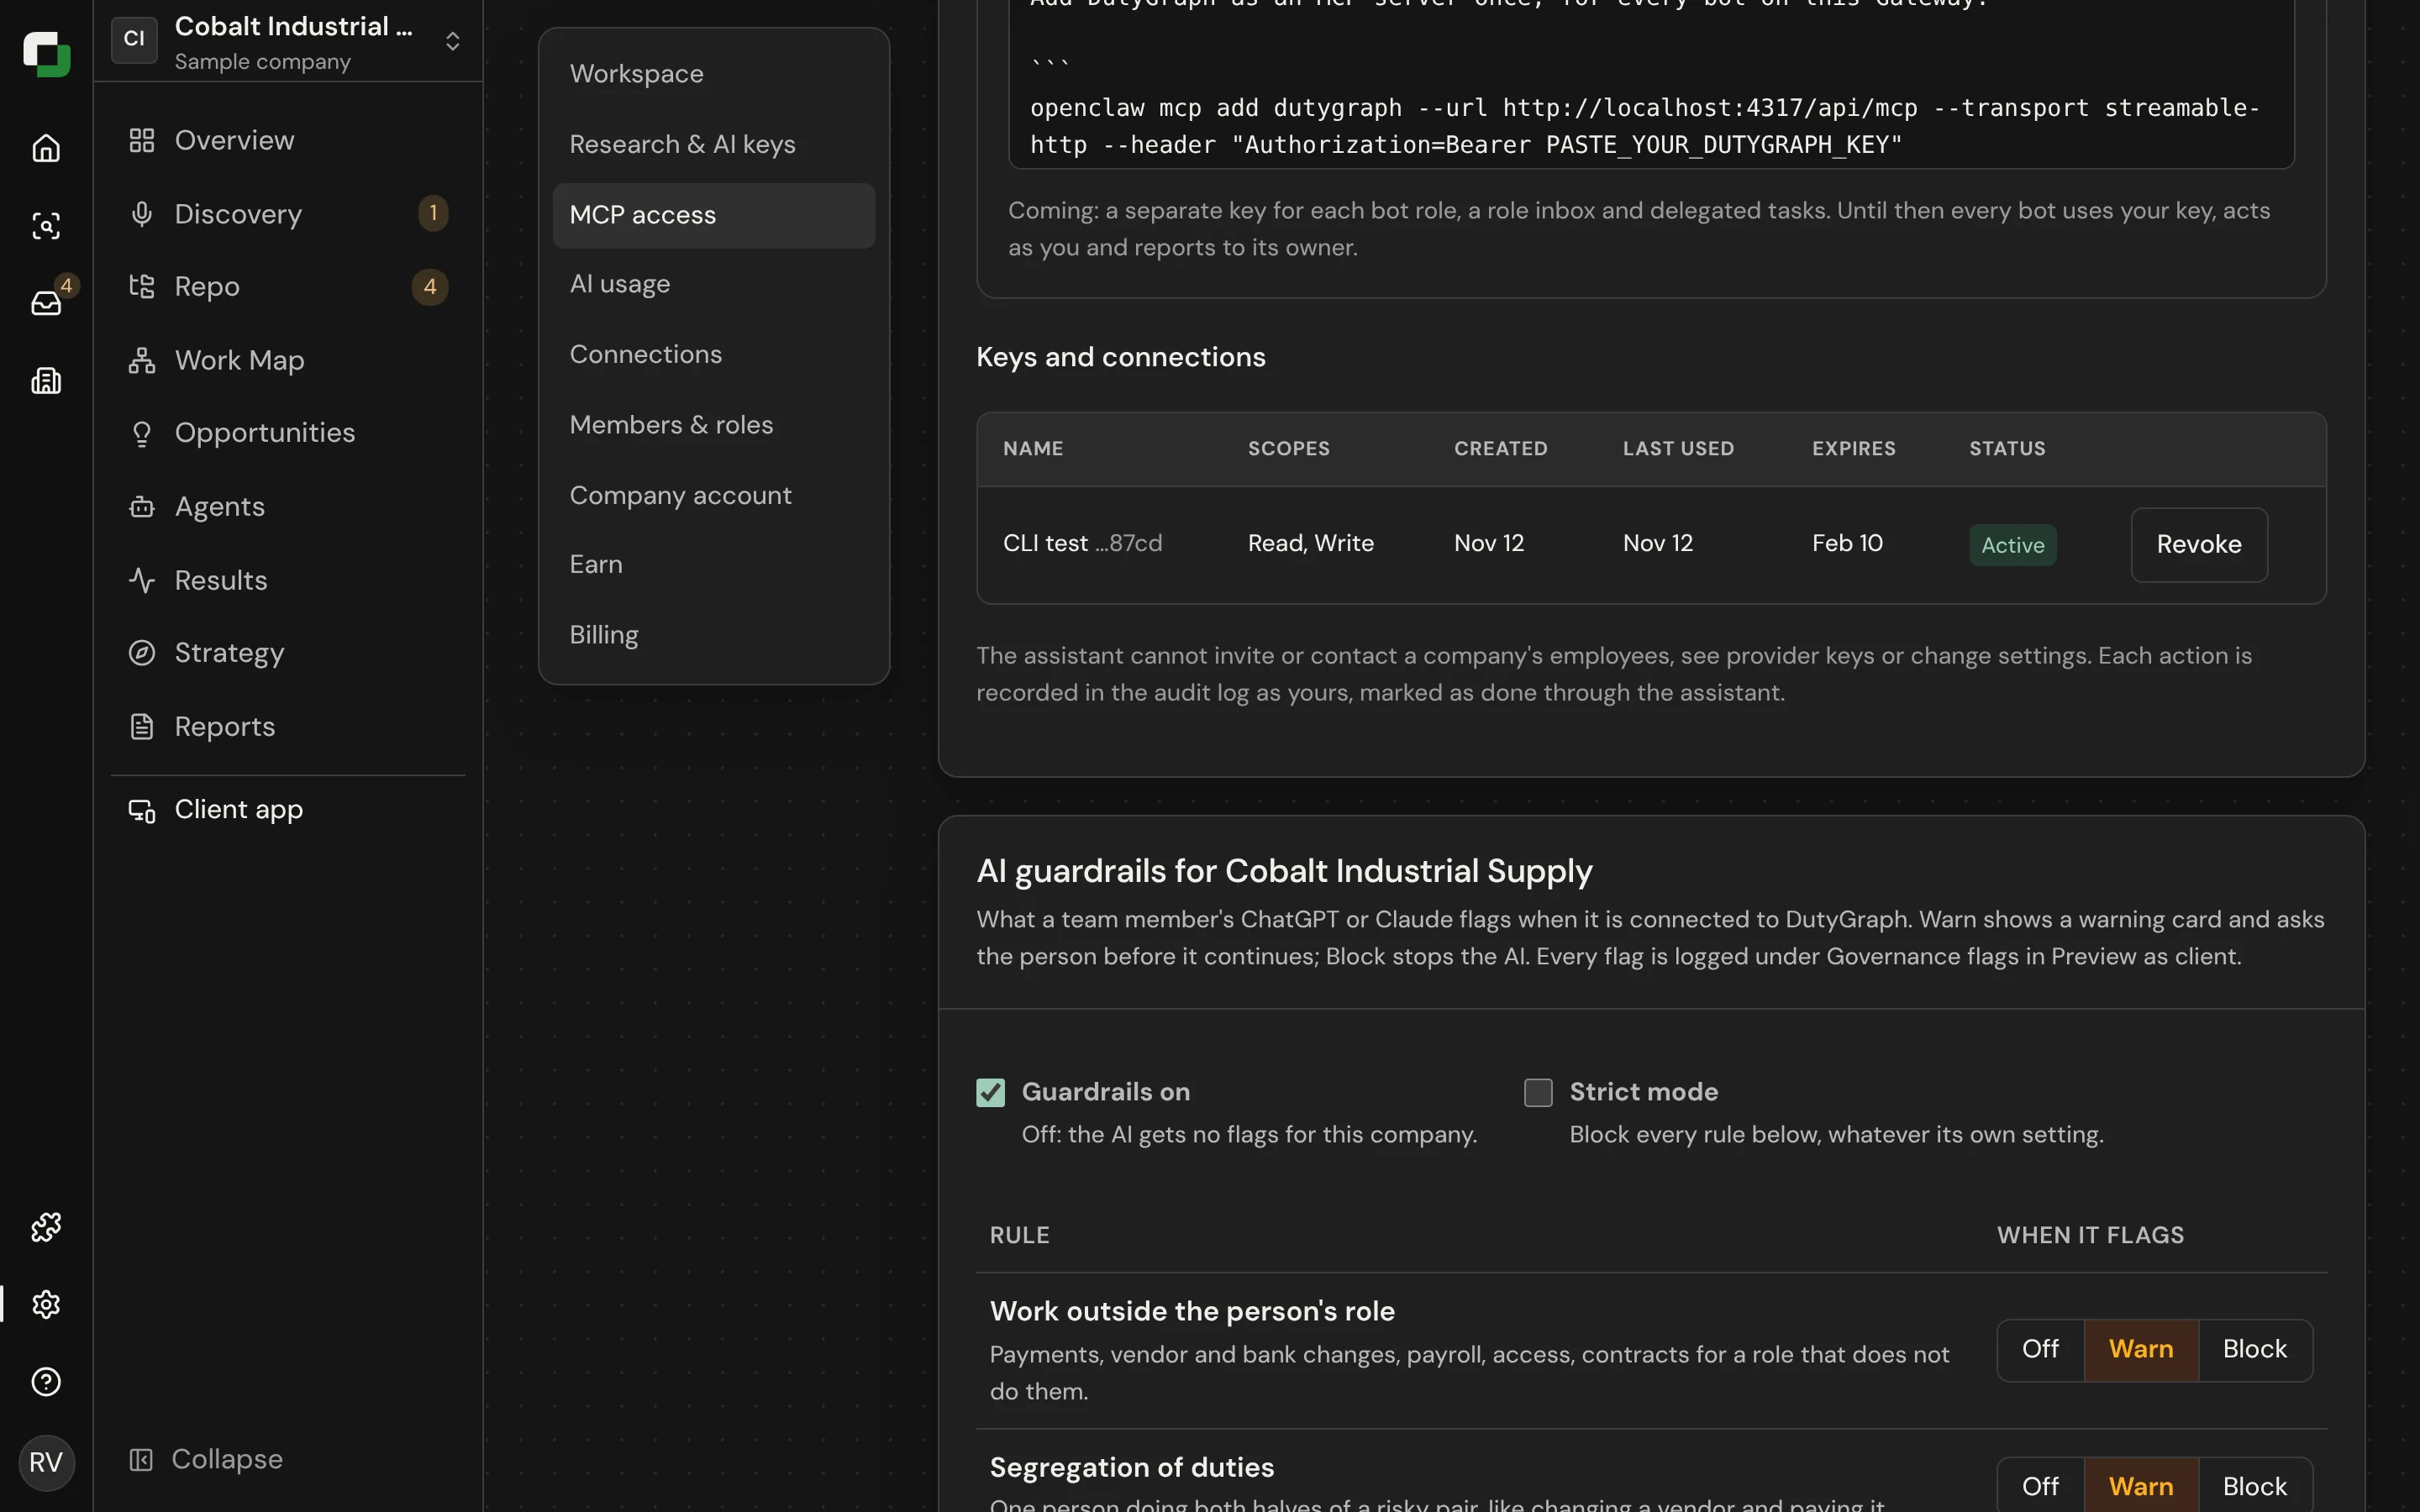
Create one in Settings › MCP access. It starts with dgp_. DutyGraph shows it once and stores only its SHA-256 hash. Revoke stops a token at once. A token cannot create or revoke tokens.
| Scope | Who | What it allows |
|---|---|---|
read | Advisor | Always on. Companies, accounts, research status, the Company Snapshot, Company Repo files and drafts. |
write | Advisor | Add accounts and people, import CSV files, start research, fill onboarding, save drafts. It does not send email. |
send_email | Advisor | Off by default. Sends a prepared draft. Turn it on only if you review each draft first. |
share_work | Employee | Send Task Card drafts for your own work |
share_strategy | Leader | Send Strategy Card drafts |
request_agents | Employee | Ask for an agent inside your own access |
The employee scopes are bound to one person and never combine with the advisor scopes.
Tokens expire after 30 days, 90 days (the default), 1 year, or never.
Limit a token to chosen companies
Built
By default an advisor token reaches every company in its workspace.
When you create a key in Settings › MCP access, Companies offers All companies in this workspace or Only the company that is open. A limited token lists only those companies. Any other company answers NOT_FOUND, and tools that add companies answer TOKEN_COMPANY_LIMIT.
Send the token
http
POST /api/mcp
Authorization: Bearer dgp_...
Keep tokens out of files you commit. Use an environment variable such as DUTYGRAPH_TOKEN.